Most MDM projects are built to solve one problem: getting customer data clean and unified. Teams spend months deduplicating records, building golden records, and connecting source systems. Then they declare success and move on.
What they rarely plan for is everything that happens next.
Customer data does not sit still once it is created. It gets updated, enriched, shared, queried, distributed to downstream systems, and, eventually, required to be deleted. Each of those moments is a governance decision. And it is where compliance failures, data quality degradation, and security incidents quietly accumulate.
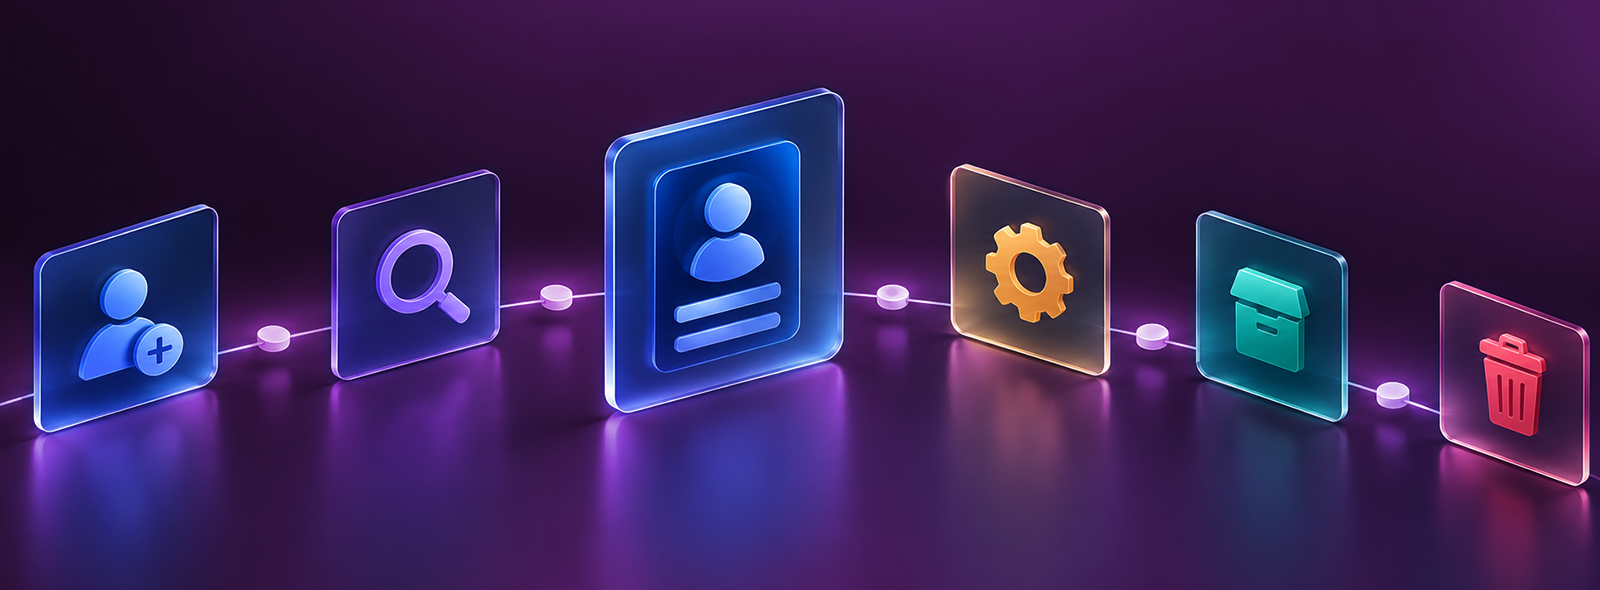
Here is what the customer data lifecycle actually looks like inside a mature customer MDM environment and what needs to be governed at each stage.
Stage 1: Creation and Onboarding
Every customer record begins somewhere. A digital onboarding flow. A branch input. A third-party data feed. A migrated legacy file. The quality problem almost always starts here. Mandatory fields left blank. Name formats that do not match any standard. A new record created for a customer who already exists in the system because no ETB/NTB check was performed at the point of entry.
A good customer MDM intercepts the record before it is committed, running validation rules, enforcing mandatory fields, and checking for duplicates against the existing base. The golden record is initiated at this stage, not built retrospectively after the damage is done.
Stage 2: Enrichment and Maintenance
A customer's data changes. They move. They change their phone number. Their KYC document expires. They add a product. They get married and change their name.
The maintenance challenge in customer MDM is propagation. When a customer updates their mobile number on your app, does that update reach your core banking system? Your collections platform? Your AML screening database? In most architectures, it does not. At least not automatically.
The result is drift. Records that were accurate at creation become stale across the estate. Three months later, a collections team is calling a number that was disconnected two years ago. A screening engine is running on an address that no longer exists. A cross-sell campaign reaches the wrong segment.
This is a maintenance governance failure in customer MDM. And what happens when there are two records with conflicting values for the same field. Which one wins? These survivorships rules need to be codified in the MDM layer. Not assumed. Not managed manually.
So, what does a good customer data lifecycle looks like? It’s continuous, real-time or end-of-day synchronization between source systems and the golden record, with survivorship rules governing conflict resolution.
Stage 3: Usage and Distribution
The golden record does not live in isolation. It feeds every downstream system: AML screening, CRM, credit decisioning, analytics, AI models, campaign management. if the golden record is not maintained in stage 2, every system consuming it inherits degraded data. The customer MDM becomes a single source of error rather than a single source of truth
The governance question at this stage is who can access what, for what purpose, and in what form. Data collected for onboarding does not automatically carry permission for marketing analytics. Access to customer records should be logged with every query, every system, every timestamp.
Stage 4: Archival and Retention
Most organizations have a data retention policy but few enforce them. A policy can say customer data should be deleted seven years after account closure. But does that deletion actually happen? Automatically, across every system that holds a copy of that record? With a log that proves it did?
Inactive records that should have been archived or deleted continue to occupy the customer MDM estate. They degrade matching accuracy. They create compliance exposure. And they make the next stage significantly harder.
Stage 5: Deletion and the Right to Erasure
Deletion is the most underbuilt stage in almost every customer MDM implementation because customer's data does not exist in one place. It exists in the MDM, the core banking system, the CRM, the data lake, the backup environment, and potentially in the AI model trained on historical records. Deleting the golden record does not delete any of those copies.
A complete erasure requires knowing where every copy of a customer's data lives, which means data discovery and mapping are prerequisites, not optional enhancements. The customer MDM should be the system that identifies every downstream location when a deletion request is triggered and coordinates the workflow across all of them.
Governance Across All Five Stages
Each stage depends on the one before it. Poor creation governance creates maintenance problems. Poor maintenance creates usage problems. Poor usage governance creates deletion problems. They compound.
What ties the customer data lifecycle together is a governance layer that spans all five stages: a unified inventory of where customer data exists, automated workflows for each lifecycle transition, audit trails that hold up under scrutiny, and survivorship rules that are consistently applied. Therefore, a mature customer MDM platform treats the data lifecycle as a continuous operational responsibility
If you want to see how PrimeMDM manages the full customer data lifecycle in a BFSI environment, contact us.